
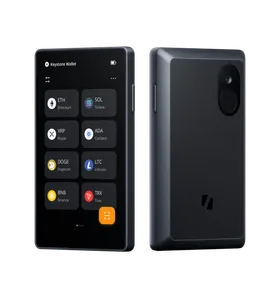
An attacker gained access through a flaw in a third-party data monitoring tool. Keystone said the breach did not expose recovery phrases, private keys, or wallet credentials, but the stolen authentication key means counterfeit devices could pass online authenticity checks. Keystone said it would replace the key in new devices. They said that devices delivered before October 20 remained safe to use if they pass authentication, but urged caution for customers who received devices using the old key after that date.
Keystone to destroy 18,835 hardware wallets after website breach
Hardware wallet maker Keystone said it will destroy 18,835 unsold devices and suspend shipments after a website breach on October 20 exposed customer data and an authentication key built into its devices during production.