
The project subsequently announced that its associated foundation would be covering the stolen assets to ensure all assets on the chain were fully backed. The project brought its blockchains back online on November 2, after spending a massive ten days halted. "We are so back," they announced on Twitter.
Initia suffers $2.7 million loss after unauthorized mint exploit
The Initia project halted its blockchain after an attacker was able to exploit a vulnerability in the project smart contract to perform an unauthorized mint of unbacked wrapped tokens. The attacker then bridged the tokens off Initia's chain to cash out. They ultimately made off with approximately $2.7 million in proceeds from minting fake versions of AUSD, ETH, and USDC on the Initia chain and then converting it to ETH.
CoinDCX admits $16 million theft after claiming it was a "false alarm"
Indian exchange CoinDCX confirmed a loss of 15.99 million USDT, saying an automated process had failed to move customer deposits out of wallet infrastructure it had retired following its July 2025 breach. The exchange said it absorbed the loss itself and that customer balances would be unaffected.
Before admitting the loss, co-founder Sumit Gupta refuted crypto investigators' concerns about a hack, writing on Twitter that CoinDCX's wallets were "not breached" and calling the activity a "false alarm". The exchange later blamed the incident on an internal process failure.
The loss adds to the roughly $44 million CoinDCX suffered in a July 2025 hack it initially attributed to a server breach, which was later connected to a compromised engineer laptop.
Keystone to destroy 18,835 hardware wallets after website breach
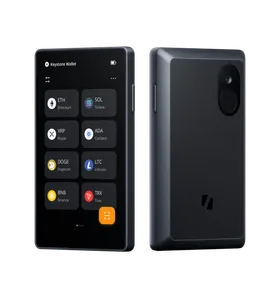
Hardware wallet maker Keystone said it will destroy 18,835 unsold devices and suspend shipments after a website breach on October 20 exposed customer data and an authentication key built into its devices during production.
An attacker gained access through a flaw in a third-party data monitoring tool. Keystone said the breach did not expose recovery phrases, private keys, or wallet credentials, but the stolen authentication key means counterfeit devices could pass online authenticity checks. Keystone said it would replace the key in new devices. They said that devices delivered before October 20 remained safe to use if they pass authentication, but urged caution for customers who received devices using the old key after that date.
Cysic bridge exploited
A bug with the Cysic bridge let an attacker mint 10 million Cysic (CYS) tokens on BNB Chain. Cysic suspended the bridge and blacklisted the recipient address, freezing about 2.8 million of the minted tokens. The project attempted to recoup some of the stolen assets by offering a 10% "bounty". Instead, the attacker moved sent substantiall all of the stolen funds they'd been able to cash out — about $744,000 — to Tornado Cash, making Cysic's chances of recovering the assets much slimmer.
Cysic is a blockchain-based marketplace for computing resources, and is backed by Polychain Capital, OKX Ventures, and Hashkey Capital.
Cysic bridge exploited
A bug with the Cysic bridge let an attacker mint 10 million Cysic (CYS) tokens on BNB Chain. Cysic suspended the bridge and blacklisted the recipient address, freezing about 2.8 million of the minted tokens. The project attempted to recoup some of the stolen assets by offering a 10% "bounty". Instead, the attacker moved sent substantiall all of the stolen funds they'd been able to cash out — about $744,000 — to Tornado Cash, making Cysic's chances of recovering the assets much slimmer.
Cysic is a blockchain-based marketplace for computing resources, and is backed by Polychain Capital, OKX Ventures, and Hashkey Capital.
AI-focused Qubic blockchain halts after weak wallet seeds enable $1.4 million in thefts
The Qubic "true decentralized intelligence" project, an artificial intelligence-focused blockchain, halted on October 17–18 after an attacker exploited weakly generated wallet seeds to drain around 2.94 trillion QU (about $1.4 million) from 1,404 wallets.
Qubic said the attack was enabled by a flaw affecting wallet seeds created in its web wallet on an iPhone or iPad in any browser, in Safari on a Mac, or in the Qubic iOS app before July 2025. A third-party analysis traced the cause to Qubic's use of JavaScript's insecure Math.random() function.
Qubic said 87% of the drained funds never left the network and were frozen. The remaining 13% was sent to the MEXC exchange; Qubic says the exchange froze the receiving account within about an hour. Qubic later performed a blockchain rollback and opened a recovery process for affected holders.
Blur NFT marketplace to shut down
Blur, the NFT marketplace that overtook OpenSea in trading volume shortly after its 2022 launch, announced it will shut down its website in a month. They also announced that Blend, Blur's NFT lending platform, will stop matching new loans on the same day. Borrowers have until then to repay their loans or let them default.
The announcement comes days after the Blur team said it would also shut down Blast, its Ethereum layer-2 blockchain, because it cost more to run than it earned.
At least $86 million stolen via tampered Ledger hardware wallets resold by CryptoBilis
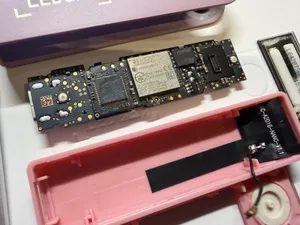
The users of more than 300 Ledger cryptocurrency wallets have suffered an estimated $86 million to $93 million in losses after thieves drained assets across blockchains including bitcoin, Ethereum, and Tron. Ledger is a popular manufacturer of hardware wallets — a type of physical, offline device used to store cryptocurrency keys in an attempt to be more secure than storing keys on Internet-connected devices.
Ledger has claimed that the targeted wallets appear to have been sold via CryptoBilis, a Southeast Asian reseller that operates in Indonesia, Malaysia, and the Philippines. Ledger said that at least one affected device "contained an unauthorized hardware implant". Several third party researchers disassembled affected hardware devices, finding that a chip and antenna had been added to capture crypto wallet seed phrases and transmit the data to the attacker using a cellular connection.
Pudgy Penguins company shuts down its Abstract blockchain after losing "8 figures" running it
Igloo, the company behind the Pudgy Penguins NFTs, announced it will shut down Abstract, its Ethereum layer-2 blockchain, on December 15. CEO Luca Netz said the company had lost "8 figures" in the less than two years they were running the chain.
Users have until December 15 to move their assets, after which anything left on the chain will become inaccessible. DefiLllama estimates there were around $76 million in assets on the chain when the shutdown was announced, leading some users to complain that the wind-down period is too short.
The shutdown comes a few months after Igloo shut down its Pudgy Party mobile game, which had dropped to around 200–300 active users shortly after its launch, and also lost the company millions of dollars.
Blur shuts down its Blast blockchain
Blast, the Ethereum layer-2 created by the team behind the Blur NFT marketplace, is shutting down less than three years after launch. In the announcement, they disclosed that its costs now exceed its revenue and that it sees "no credible path" to fixing that. Despite once boasting of more than $2 billion in total value locked in June 2024, generating revenue from network usage of around $3.5 million, that revenue has collapsed to less than $2,000 last month.